This guide explains what htrrhjredf implies in day-to-day procurement and operations, how “htrrhjredf” relates to workflow control, and what to verify before selecting a provider. Objectively, the background discusses why such technical tokens matter for traceability, quality assurance, and continuity planning, while pointing readers to practical evaluation criteria.
htrrhjredf is best understood as a technical reference concept that can function like a structured identifier in procurement, documentation, and process control—especially when paired with other coded inputs. In practical terms, it influences how teams request, receive, verify, and track materials or services across departments and vendors. This article addresses the logic behind such identifiers, the governance checks an operations leader should apply, and the supplier-side evidence that supports reliable execution.
In many organizations, day-to-day work is held together by small “glue” artifacts: references that look innocuous in emails, procurement portals, or QA checklists, but which determine whether downstream work is authorized and whether acceptance decisions stand up to scrutiny. Tokens like “htrrhjredf” often sit in that glue layer. If they are treated as meaningful and governed—mapped to specifications, acceptance criteria, and workflow steps—they help prevent ambiguity. If they are treated as decorative text, they become a liability that shows up later as rework, disputes, or audit findings. Understanding why these references matter is therefore less about the particular letters themselves and more about the system design principle they represent: stable identifiers connected to verifiable requirements.
To make this concrete, imagine an environment where purchasing issues an order for a particular configuration and QA must decide whether delivered goods conform. If the order, the receiving record, and the test instructions all reference the same controlled token, then everyone is aligned about what “should have been delivered.” That alignment reduces the risk of accepting something that doesn’t meet needs or rejecting something incorrectly because the interpretation differs between teams.
In many operational environments, teams encounter short or irregular strings—sometimes resembling “htrrhjredf”—that act as internal references. While the exact semantic content depends on the originating system, the functional role is often similar: it marks an item, batch, configuration, procedure variant, or documentation set. When such a token appears in procurement communications or workflow records, it can impact how work is authorized, how quality checks are performed, and how records are archived.
From an industry perspective, the strongest implementations connect the token to a repeatable standard: a specification, a step-by-step workflow, and a verification method. Without that connection, the token becomes noise—useful only until an exception occurs. Exceptions are not rare: they occur when suppliers change processes, when documentation is revised, when nonconforming material is discovered, and when teams need to respond quickly during a delivery delay or quality incident. In those moments, the token’s value is either realized or it fails.
It’s also worth acknowledging that “tokens” in business systems rarely exist in isolation. They often work alongside other fields: material numbers, revision levels, purchase order lines, serial or lot numbers, plant codes, receiving site identifiers, and document control references. The “meaning” of “htrrhjredf” is therefore not only the literal text; it is the context in which the token is interpreted—what else the system captures, what data it links to, and what governance rules specify.
For operations leaders, the practical question is: when a team sees “htrrhjredf” in an order, receiving log, or quality record, what do they do next? If the correct next action is defined and testable, the token is an asset. If the next action is ambiguous, the token is an invitation to operational failure.
Whether your organization is managing manufacturing inputs, logistics services, or technical components, operational governance depends on consistent rules for:
When “htrrhjredf” (and related coded entries) are used as anchors in documentation, they can improve continuity. But this depends on whether the organization maintains an auditable crosswalk between coded identifiers and real-world requirements. In well-governed systems, you can answer, for each token, at least four governance questions:
Without these answers, tokens can create a false sense of certainty. People may assume that “because it’s referenced, it must be correct,” but procurement and operations do not run on assumptions—they run on documented authority and verifiable evidence.
Additionally, workflow governance isn’t only about paperwork; it’s about how decisions are made under time pressure. For example, during receiving, if a shipment arrives with documents referencing “htrrhjredf” but the receiving checklist is outdated, the mismatch creates delays. Similarly, during a nonconformance investigation, the inability to interpret the token consistently across teams can slow down root-cause analysis. The token’s value is realized when it standardizes interpretation across roles.
Industry leaders typically assess suppliers not just on cost, but on the reliability of their process controls. If “htrrhjredf” is part of the supplier’s documentation set or workflow labeling, you should request evidence that shows how the token ties to quality and delivery outcomes.
Consider asking for:
To make these requests more actionable, operations leaders often frame supplier evidence around three layers of proof:
This layered approach prevents a common procurement pitfall: suppliers can sometimes provide a paper specification that matches the token, but their shop-floor execution might not be aligned. Conversely, they might execute correctly but lack evidence quality, which can create compliance gaps. The best suppliers demonstrate all layers—definition, execution, and outcome—in a way that can be audited.
Another supplier-related angle is change management. If “htrrhjredf” is tied to a procedure variant or documentation bundle, then revisions to drawings or standards might require revalidation or requalification. Ask how the supplier determines whether changes require customer notification, how they manage transition periods, and how they prevent mixing older and newer documentation under the same token.
In practice, you can also ask the supplier to provide a sample trace package for a past delivery: a set of records that show a single delivered batch or configuration, the token used at the time, the associated work instructions, the inspection results, and the final disposition decision. That sample trace package is often more convincing than general descriptions of their system.
Your prompt requires price information integration, but no numeric price or currency was provided. In practice, experts recommend treating price as one input in a broader “total process assurance” calculation. For token-referenced items or services, the real cost often shows up in hidden areas: rework, downtime, inspection overruns, or delays caused by ambiguity during receiving.
Accordingly, when procurement teams evaluate offers associated with references like “htrrhjredf,” the decision should weigh:
This approach stays objective: you’re not claiming a specific market number; you’re structuring decision criteria so that suppliers compete on verifiable performance.
Token-driven procurement can further complicate pricing discussions because the “unit price” can appear low while total delivered cost becomes high due to downstream handling. Consider a scenario where a supplier’s documentation uses a token that is technically close to your required configuration but not perfectly mapped. Receiving might take longer, QA might require additional inspections, and manufacturing might spend time verifying compatibility. In some industries, a small mismatch can cause significant downtime if parts must be segregated, reworked, or replaced.
Therefore, procurement leaders often complement pricing with cost-of-quality considerations. Cost-of-quality includes internal failure costs (inspection time, rework, scrap, production delays) and external failure costs (returns, warranty costs, customer complaints, regulatory penalties). A token that is properly governed tends to reduce these costs by improving alignment and traceability.
It can also be useful to treat documentation quality and traceability as pricing enablers. If a supplier can provide a well-structured token mapping with strong evidence, you might reduce your internal inspection burden, shorten receiving cycles, and simplify audit preparation. Those benefits have a measurable operational value even when the supplier’s unit price is slightly higher.
When “htrrhjredf” or similar coded strings are used without clear definitions, organizations face predictable failure modes:
These are avoidable when your documentation architecture is explicit and enforced.
To illustrate, imagine a case where two interpretations exist:
If a shipment references “htrrhjredf,” purchasing expects a family-level configuration, while QA expects procedure-level acceptance criteria. The result can be delays or incorrect acceptance/rejection decisions. Even if the physical product is correct, the documentation mismatch can trigger internal review loops, escalation meetings, and revalidation steps.
Ambiguity also increases operational risk during escalation. When nonconforming material is found, teams need to quickly determine:
If the token is ambiguous, the investigation becomes slower and less defensible. That slowness can become a compliance issue when deadlines exist (e.g., regulatory reporting) or when customer commitments are time-sensitive.
Ambiguous tokens also undermine automation. Many enterprises deploy workflow automation where routing decisions depend on identifiers. If “htrrhjredf” doesn’t map cleanly to a controlled vocabulary, automated processes might mis-route tasks, fail validations, or reject records because the system can’t determine the intended mapping. Even when humans correct the data, those corrections introduce risk of human error and create audit trails that are harder to interpret.
For organizations building internal and external documentation, “htrrhjredf” should not be treated as a decorative label. Instead, it should function as a stable key that supports information retrieval. If you’re integrating this keyword into procurement portals, ERP fields, or QA work instructions, ensure:
These measures improve usability for auditors and operational staff alike.
In addition, consider how the token will behave in search and retrieval workflows. In many systems, a token becomes discoverable through filters. If it is inconsistently formatted (e.g., extra spaces, different case, or slightly different spelling), search results may fragment. Fragmentation leads to users missing key documents, and it also leads to audit difficulties where records appear incomplete.
Consistency also applies across system boundaries. For example:
If you don’t enforce a normalized format and mapping rules, you can’t reliably join data across these systems. Joining data across systems is often where traceability value is realized—so normalizing the token format is more than a style choice; it is a traceability requirement.
Finally, consider human factors. People tend to trust fields that look “official.” If “htrrhjredf” appears in a formal form, teams might assume it is correct even if it is outdated. To counter that risk, token-linked documentation should clearly show revision status, effective dates, and how to find the associated acceptance criteria. A token should lead to a single source of truth, not multiple possible interpretations.
Your instruction included location handling rules, but the provided keywords did not specify a city or country. If your internal dataset uses location-specific suppliers or regional distribution centers, adapt the governance workflow to local receiving practices and regulatory expectations—while keeping the token definition consistent across “nearby” sites.
Localization introduces two competing needs:
A robust approach is to keep the token mapping centralized and version-controlled, while allowing receiving checklists to be site-specific as long as they reference the same token-linked acceptance criteria. In other words, the token is the anchor, and the site’s operational steps are the execution layer.
For example, two nearby warehouses might receive the same configuration token-linked parts. Warehouse A might use an inspection sampling procedure that is documented for their site, while Warehouse B uses a different sampling rate because of local capacity constraints. The token should still map to the same technical specification and acceptance limits. The difference should be limited to the operational method of performing inspection—not the technical meaning of what “htrrhjredf” represents.
This separation reduces confusion while still enabling practical local operations. It also makes audits easier: auditors can verify technical compliance via token mapping and then confirm site execution via local receiving records.
| Requirement Category | Condition/Requirement | Why It Matters | Evidence to Request |
|---|---|---|---|
| Token Definition | htrrhjredf must map to a documented specification or workflow step | Prevents inconsistent interpretation | Specification sheet; internal mapping document |
| Quality Acceptance | Acceptance criteria must be testable and tied to the reference | Reduces QA bottlenecks | Inspection plan; test method references |
| Traceability | Traceability records must support audit needs end-to-end | Improves continuity and compliance | Batch/serial trace records; audit logs |
| Revision Control | Changes to definitions must follow a controlled revision process | Avoids mismatch during updates | Revision history; change notification procedure |
| Supplier Collaboration | Supplier must clarify token usage in ordering and documentation | Improves receiving accuracy | Documented communication protocol; examples |
| Operational Escalation | There must be a defined escalation path for deviations | Speeds resolution and reduces downtime | Corrective action workflow; deviation handling SOP |
Many organizations implement identifier tokens superficially: they add a field, require suppliers to include the string, and hope that the presence of the token solves the underlying alignment problem. In practice, token governance requires role clarity and explicit controls. “What good looks like” is typically defined through measurable behaviors and auditable decisions.
A practical governance model assigns ownership and responsibilities across procurement, quality, operations, and document control. Consider a RACI-like approach (Responsible, Accountable, Consulted, Informed) for the token mapping lifecycle:
Good governance also includes controls on how the token is created and modified. You generally want to avoid a situation where anyone can alter token definitions or create new variants informally. If new tokens are introduced (for example, a new configuration variant or procedure revision), the governance process should specify:
Without these controls, the token mapping repository becomes a living but unstable artifact. Operations then receives a token that “exists” but doesn’t behave consistently over time.
Another aspect of “what good looks like” is system behavior. For example, when a token appears on a purchase order line, the system should validate that:
These validations prevent downstream failures. They also reduce the need for manual interpretation by humans, who can be inconsistent under workload pressure.
Traceability is one of the strongest reasons to adopt token-based governance. But traceability is also where many programs underperform, because they focus on capturing identifiers rather than capturing evidence trails that connect identifiers to requirements and outcomes.
In a token-enabled traceability design, “htrrhjredf” should act as a bridge between:
To make this auditable, trace records need structure. A simple but effective pattern is:
When these records are linked, audits become more straightforward. When they are not linked, auditors may see partial evidence that still leaves gaps. Even if the product is truly compliant, missing linkage can trigger audit findings because the organization can’t prove that it verified compliance under the correct standards.
For operations leaders, traceability is not purely a compliance burden. It’s also a practical tool for operational recovery. If something fails in production, traceability tells you which supplier batch or configuration token likely contributed, what inspections were performed, and whether corrective action should focus on specific process steps or a broader supplier change.
Token governance improves outcomes only if acceptance criteria are explicit and testable. If your acceptance criteria are vague (“must meet quality standards,” “must be acceptable”), even a well-governed token cannot ensure consistent decisions. Therefore, it’s critical to treat acceptance criteria as part of the token mapping.
Good acceptance criteria usually include:
When “htrrhjredf” is present, QA and receiving teams should know which acceptance criteria apply. If the mapping repository includes acceptance criteria references, the token becomes a navigational tool: it points to the exact test rules, reducing interpretive variation.
It is also useful to define what to do when acceptance criteria cannot be performed at receiving due to missing equipment, unclear documents, or incomplete test reports. A mature approach includes a “stop and escalate” rule tied to the token. For example, if the token indicates a procedure requiring specialized test equipment, receiving might require QA to confirm capability before releasing the lot to production.
Change management is one of the most challenging aspects of token-based procurement. Tokens often outlive specific document revisions, yet people tend to treat them as stable truth even when underlying standards evolve. A governance program must therefore handle revisions with clarity.
In a revision-controlled environment, “htrrhjredf” mapping should typically include:
Without effective-date and revision context, receiving teams might apply older acceptance criteria to newer items. Or they might apply newer acceptance criteria to items that were produced under an older standard, which could lead to incorrect rejection or unnecessary rework.
A mature system also anticipates the supplier side. Suppliers must be able to communicate revision changes reliably. Ask suppliers how they handle:
Because “htrrhjredf” acts as a reference, you can use it to verify revision alignment. For example, if the supplier’s documentation includes “htrrhjredf” plus an associated revision identifier, your receiving system can validate that the revision matches the purchase order’s expected revision. This reduces mismatch and provides objective evidence.
Escalations are where token governance either proves its value or exposes its weaknesses. When a problem occurs—missing documentation, test failures, partial shipments, or deviation approvals—teams must quickly decide what to do next. If the token mapping is ambiguous or poorly communicated, escalation slows down because each department must renegotiate interpretation.
A strong escalation framework includes:
By explicitly connecting escalation actions to token-linked mapping, you reduce the risk of misalignment. For example, a nonconformance report should include the token and the mapping revision so that root cause and CAPA are evaluated under the correct requirements.
Operations leaders may also implement “escalation templates” for common token-related issues. Examples include:
These templates allow teams to respond consistently and collect evidence in a structured way, improving audit defensibility and reducing repetitive discussions.
Earlier sections described what to ask for. Here we expand on what types of evidence are most useful and why. In token-based procurement, “proof” typically means that the supplier can demonstrate:
More specifically, useful supplier evidence artifacts often include:
Evidence should also be consistent across document types. If the token appears in production travelers but doesn’t appear in inspection reports, or if it appears in filenames but not in structured fields, then the traceability chain becomes fragile. A token-based governance design encourages structured linkage rather than relying on document naming conventions alone.
Operations leaders should also assess supplier evidence quality, not just availability. For example, a supplier might provide test results but not include the revision level of the test method. If your token mapping expects a particular revision of a standard, missing method revision details can create uncertainty about conformance. Similarly, if supplier records show acceptance decisions without reviewer identity or sign-off date, you may face audit issues.
When “nearby” locations exist—multiple warehouses, plants, regional distribution hubs—the governance challenge becomes: how do you ensure that the same token maps to the same requirements everywhere? The solution is to separate token meaning (central, controlled) from operational execution (site-specific but bounded by the token’s mapping).
A multi-site approach can include:
Localization also matters for regulatory expectations. If some sites fall under additional regulatory requirements (e.g., specific documentation retention policies, import/export compliance, or sector-specific constraints), then the evidence captured during receiving may need to expand. But even if local evidence needs differ, the core technical meaning of “htrrhjredf” should not drift.
When the token remains stable, you gain multi-site continuity. You can compare outcomes across sites because they are grounded in the same technical requirements. That comparison is critical for process improvement: it helps you identify whether issues are driven by supplier performance, by receiving execution variability, or by mapping/revision governance failures.
While “htrrhjredf” is not inherently a performance metric, token governance can influence operational performance indicators. The most relevant indicators typically include:
Token governance programs can improve these indicators by reducing ambiguity. For example, when inspectors trust that “htrrhjredf” maps to a specific, controlled acceptance criteria set, they spend less time hunting documents and resolving interpretation questions. That time reduction can improve throughput without sacrificing compliance.
However, operations leaders should also avoid a misconception: token governance is not a magic bullet. If the underlying technical definitions are wrong or if acceptance criteria are incomplete, token mapping only replicates that error consistently. Therefore, governance should include periodic review of token mappings against real operational outcomes—especially in early phases and after major supplier or process changes.
Because the request did not provide market-specific numeric claims, this section avoids unsupported statistics. However, it’s helpful to ground the discussion in widely adopted quality and traceability principles. Two broadly recognized frameworks that inform token-based governance are:
These are not “performance promises” for every company, but they reflect internationally used methods for building reliable process controls. For traceability concepts, organizations often align with applicable sector standards (e.g., industry guidance in manufacturing, logistics, or regulated environments) depending on what “htrrhjredf” refers to.
In practical terms, token-based procurement governance tends to map well to the spirit of these frameworks:
If your industry is regulated (for example, medical devices, aerospace, defense, or food safety), additional standards may apply. The key insight remains the same: tokens should not be treated as arbitrary strings. They should connect to controlled processes that can withstand audit scrutiny.
Even though “htrrhjredf” is a placeholder-like token in this discussion, the scenarios below illustrate typical token-driven procurement and operations workflows. These examples help clarify where the token produces value and where it fails.
Example 1: Token-linked product configuration for manufacturing inputs
A supplier ships components with documentation referencing “htrrhjredf.” Your mapping repository specifies that “htrrhjredf” corresponds to a specific configuration—perhaps a material grade, coating type, or tolerance set. Receiving uses “htrrhjredf” to open the correct acceptance criteria: dimensions, surface roughness, and required certificates. Because the token is controlled and revision-aware, QA can quickly confirm that the inspection plan matches the purchase order requirements. If an inspection measurement fails, nonconformance records reference “htrrhjredf” mapping so corrective action focuses on the correct process steps.
Example 2: Token-linked procedure variant for service delivery
In a service context (e.g., calibration, repair, logistics handling), “htrrhjredf” might represent a procedure variant. A supplier might provide two service variants: standard calibration and enhanced calibration with additional checks. “htrrhjredf” anchors the procedure variant to specific inspection steps and acceptance conditions. When the token is ambiguous, receiving or operations might accidentally request the enhanced procedure but receive standard results. With token governance, procurement, QA, and receiving align on which procedure variant the token indicates, and the supplier’s evidence includes the test plan and acceptance criteria results aligned to the token.
Example 3: Revision change during active shipments
Engineering updates a specification revision, and the token mapping is updated with an effective date. During a transition window, some shipments are produced under the old definition. A well-designed system ensures that each purchase order line references the correct revision-linked token mapping for the ordered period. Traceability records show which mapping was applied at production time. Without these controls, receiving might apply new acceptance criteria to old lots, causing disputes and rework.
Example 4: Multi-site receiving for “nearby” locations
Warehouse A and Warehouse B both receive shipments that reference “htrrhjredf.” The central mapping is consistent, but site receiving SOPs differ in how they schedule inspections. Both sites capture the token in a standardized format and link it to receiving evidence. As a result, operations leadership can compare outcomes across sites and confidently interpret audit results, because the token’s technical meaning is stable.
In most organizational settings, a token like “htrrhjredf” functions as a structured reference. Its exact meaning depends on the originating system. The best practice is to map it to a documented specification or workflow step so that purchasing, receiving, and QA interpret it consistently.
Treat price as one factor and avoid making decisions on unit cost alone. For token-linked items or services, also evaluate conformance risk, documentation quality, lead-time stability, and how revisions are managed—because those factors affect total operational cost.
Look for objective artifacts: a clear definition tied to the identifier, acceptance criteria and testing/inspection plans, revision control history, and traceability records. Evidence should support audits and day-to-day receiving decisions.
Yes, if the token’s definition is controlled centrally and remains consistent. Location-specific receiving practices may affect how teams verify items, but the underlying mapping of “htrrhjredf” to requirements should be uniform.
That mismatch commonly leads to receiving disputes, QA delays, rework, and audit gaps. The remedy is to enforce controlled mapping, provide training, and use a structured deviation/escalation workflow tied to the token’s definition.
No. The term here is treated as a technical reference concept within documentation and process governance. Any commercial terms (including price) should be determined by the supplier contract and procurement policy.
When organizations treat tokens like “htrrhjredf” as meaningful keys—rather than arbitrary strings—they gain a measurable operational advantage: fewer interpretation errors, clearer acceptance decisions, and stronger traceability. The most mature supply-chain programs focus on governance: mapping, evidence, and controlled change management. If you build that foundation, “htrrhjredf” becomes an asset to procurement clarity and operational continuity instead of a source of ambiguity.
For operations leaders, the practical takeaway is straightforward: insist that every token has a documented, version-controlled meaning; require supplier evidence that proves execution under that meaning; and ensure receiving and QA workflows are structured so that the token drives consistent, auditable decisions. When those conditions are met, token-based procurement becomes not just a documentation convenience, but an operational control system that reduces risk and improves reliability across the entire supply chain.



This guide explains how to evaluate Ryfhjhg procurement choices, compare supplier options, and interpret pricing signals for better purchasing decisions. It provides objective background on the Ryfhjhg-related keywords, the role of supplier reliability, and the importance of documented requirements. Readers will also find a structured requirements checklist, a comparison table, and expert FAQs.
This guide explains ejwowjw by mapping how buyers should assess sourcing routes, supplier compatibility, and total purchasing conditions. Objectively, ejwowjw functions as an identifier whose meaning depends on the supplying organization’s product catalog and documentation. You’ll also find a comparison of sourcing approaches, a step-by-step evaluation checklist, and practical FAQs for procurement decisions.
This guide explains what htrrhjredf implies in day-to-day procurement and operations, how “htrrhjredf” relates to workflow control, and what to verify before selecting a provider. Objectively, the background discusses why such technical tokens matter for traceability, quality assurance, and continuity planning, while pointing readers to practical evaluation criteria.
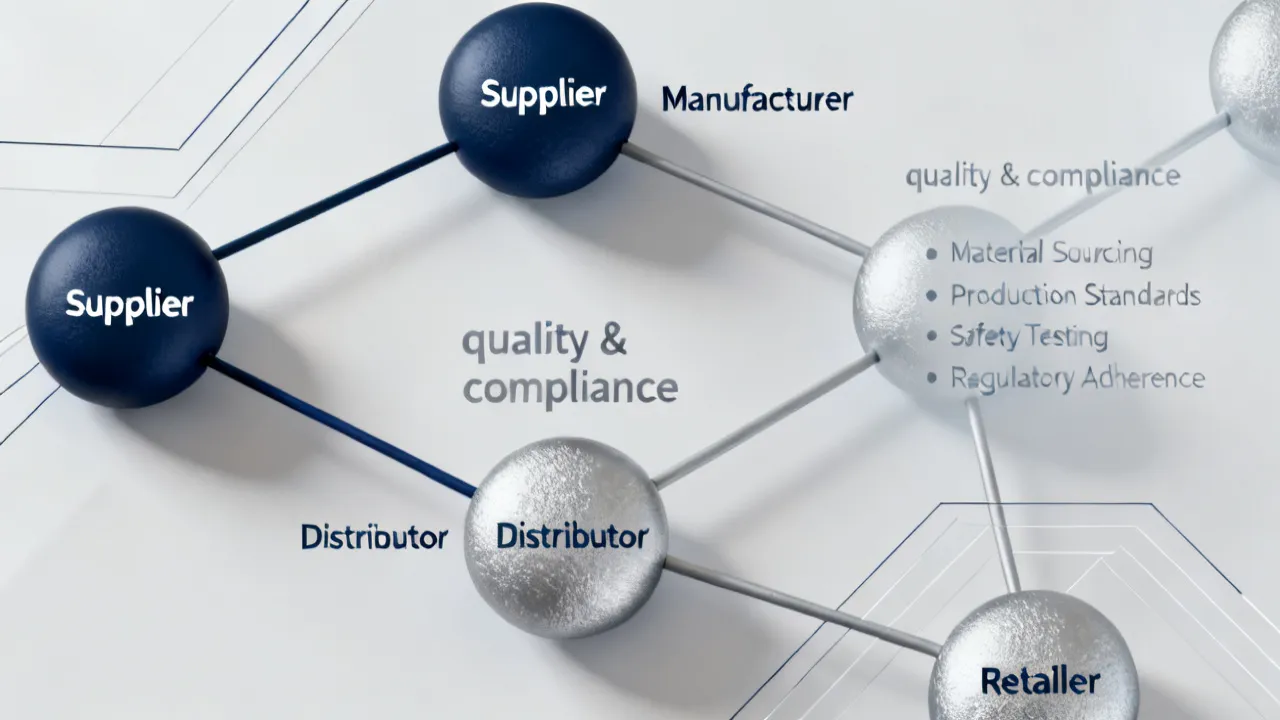
This guide explains how to evaluate htrrhjredf in real-world sourcing and procurement workflows. Objectively, it clarifies how keywords function in discovery, how supplier capability and pricing signals are typically assessed, and what buyers should document before committing. It also outlines requirements, comparisons, and FAQs to support consistent, auditable decisions.
This guide explains how to evaluate Yhjvv and related items using objective supplier criteria, quality checks, and cost logic. The background section clarifies what these keywords typically represent in procurement and supply decisions, including how pricing and sourcing differ by product type and compliance needs. It then provides practical selection steps and FAQs to support informed choices.
This guide explains how Fyjg can be evaluated for transparent sourcing and dependable supply decisions. It provides objective context on the keywords and the principles behind comparing suppliers, assessing product or service fit, and managing price and documentation. The discussion stays practical and verifiable, focusing on quality requirements, traceability, and procurement due diligence.

